
Fractional CISO · AI-native startups
Security that holds while you build.
Trellis is a hands-on security practice for companies that build fast. Trellis ships the controls, the tooling and the evidence your customers ask for; you keep shipping product.
Security leadership built at
- Charles Schwab
- Meta
- Roblox
Large enterprises have a CISO, a security team and the budget to match.
The same attackers and auditors come after you anyway.
You shouldn’t need $1B in revenue to afford security that works.
Security that holds while you build.
Where clients start
Most companies call Trellis for one of three reasons.
You need SOC 2, ISO 27001 or another framework in place before a customer, auditor or investor asks for it.
Compliance programs →You don’t know how mature your security is, or where an attacker would get in.
Security assessment →You want enterprise-grade security leadership, but you don’t need a full-time CISO.
Security leadership →Trellis is the wrong fit for a company that wants check-box compliance. Read how Trellis works →
Services
Executive judgment and engineering hands, in one engagement.
Every engagement ends with controls running in your environment and the evidence to prove it.
01
Security leadership
A fractional CISO on retainer who owns your security roadmap, compliance program, customer reviews, vendor risk, incident readiness and board reporting.
Learn more →02
Security assessment
A two-week review of your cloud, code, identity, vendors and AI systems that shows how mature your security is and where an attacker would get in.
Learn more →03
Customer security reviews
Get a stalled enterprise deal through the buyer’s security review, then answer the next questionnaire in hours instead of weeks.
Learn more →04
Compliance programs
SOC 2, ISO 27001, ISO 42001, AIUC-1, SOX IT controls and privacy programs, with controls built in your systems rather than written into a binder.
Learn more →05
AI and agent security
Limit what your AI agents can reach and do, and put your security rules inside the AI coding assistants your engineers already use.
Learn more →06
Cloud, code and platform hardening
Lock down your cloud, find the exploitable flaws in your code, and secure Google Workspace, Microsoft 365, Slack, GitHub and Salesforce.
Learn more →07
Security tools and testing
Choose the right SIEM, EDR, MDR or other tool for your stage, run the rollout until it works, and manage penetration tests your customers accept.
Learn more →08
Incident response
An incident plan and executive tabletop exercise before anything happens, and an experienced incident commander within 24 hours when it does.
Learn more →09
M&A and due diligence
Sale readiness before a buyer’s security team arrives, diligence on acquisition targets and vendors, and an OSINT scan that shows what an attacker sees first.
Learn more →The difference
Most advisors hand you recommendations. Trellis hands you tooling.
Trellis builds assessment skills and MCP servers that run against your code, cloud and SaaS configuration. You get a repeatable scan on day one, not a quarterly slide deck.
The assessment runs again every quarter, so the findings stay current instead of going stale in a PDF. You keep the fixes, the evidence and a program your team can run.
$ trellis assess --scope github,aws,workspace

✓ GitHub org        branch protection, secrets, actions
✓ AWS accounts      IAM, public exposure, logging
✓ Google Workspace  admin roles, sharing, OAuth apps

HIGH  Agent service token can write to prod DB
HIGH  Org-wide OAuth grant to unvetted AI app
MED   CI workflow exposes secrets to forks

→ fix plan, owners and evidence pack written
How an engagement runs
Assess, harden, then run it like it’s yours.
Every engagement is scoped to your organization, its size and its risk. Most clients start with a two-week assessment, move to a monthly retainer, and add fixed-price projects when a specific gap needs closing.
01
Assess
Trellis tooling scans code, cloud and SaaS. You get a ranked risk register tied to the deals, customers and data each risk puts in play.
02
Harden
Trellis fixes the top risks directly alongside your engineers: configuration changes, pull requests and identity cleanup.
03 · Ongoing
Operate
Fractional CISO coverage: board updates, customer questionnaires, audit evidence and incident response. The assessment reruns every quarter.
Founder
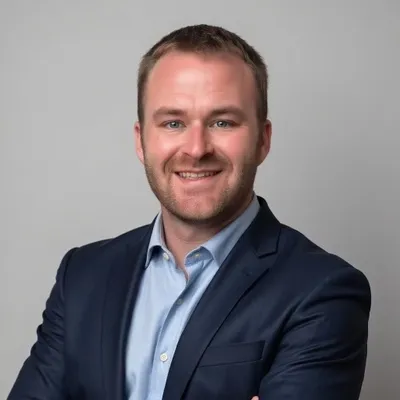
Nick Giedt
Nick led security at Roblox and at a global consumer fitness platform, ran trust and security risk programs at Meta and LinkedIn, and spent nine years as a software engineering leader at Charles Schwab. He holds a CISO Certificate from Carnegie Mellon.
Nick started Trellis after watching startups and enterprises put AI agents into production faster than their security teams could keep up. Most vCISOs would hand those companies a SOC 2 checklist. Nick builds the controls himself.
In their words
Founders, operators and engineers on working with Nick.
Nick understands the security challenges unique to AI agents better than anyone we’ve worked with. His review of our architecture was thorough, pragmatic, and directly shaped what we’re building next. Highly recommend.
Ray Zhou
Serial founder · Stealth AI startup
Nick combines deep cybersecurity expertise with a practical, accessible approach. He has helped us better understand our risks and identify clear, proportionate steps to strengthen our cybersecurity practices. He is thoughtful, responsive and extremely easy to work with.
Jenna Mander
Head of Business Operations · Nature For Justice
Nick hired me into [the company’s] first dedicated D&R role and was hands-on enough to see my work through a major incident investigation firsthand, not just review it from a distance. He’s exactly the kind of security leader who understands both the technical depth and the business tradeoffs, which is rare, and exactly what fast-moving AI-native teams need.
Sam Luu
D&R Engineer · a16z
Insights
Writing on AI security and agent identity.
Detection & response · LinkedIn
Why Agents Are Eroding the Strongest Signals in the SIEM
Coding agents now run the same LOLBins and credential-store reads attackers use, so detection has to stop asking which binary ran and start asking which identity ran it, under whose authority.
AI-generated code · LinkedIn
Governing AI-Generated Code in the Enterprise
Neither zero-trust allowlists nor trust by default can govern coding agents; keep the capability surface broad and evaluate each action by who drives it, where, what data it touches and whether it can be undone.
Agent identity · Substack
Agent Identity: Where Canonical Patterns Hold, and Where They Don’t
SPIFFE, OAuth, OIDC and policy engines still secure agent systems; the gaps open where an agent acts for a user, and closing them takes capability tokens, provenance-tagged logs and tool-level policy.
Questions
What founders ask first.
What does a fractional CISO do?
A fractional CISO owns your security program part-time: strategy, risk decisions, board and customer communication, and incident leadership. Trellis adds hands-on engineering, so the program ships instead of stalling in a backlog.
Who is Trellis for?
Companies from seed through Series D, from 5 people to more than 500, in any industry. Some have no security function yet; others have a team but no executive leading it. Trellis has particular depth with AI-native companies.
How is this different from a compliance automation platform?
A platform tracks whether controls exist. Trellis decides which controls matter for your business, implements them in your environment, and then feeds the evidence to whatever platform you use.
How long does an engagement take?
Every engagement is scoped to your organization, its size and its risk. Most clients start with a two-week assessment, move to a monthly retainer, and add fixed-price projects when a specific gap needs closing before a customer deal, an audit or a funding round.
Do you work with companies outside AI?
Yes. Trellis also supports nonprofits, defense suppliers preparing for CMMC, and growth-stage SaaS companies.
Build fast. We’ll make sure it holds.
Thirty minutes. Bring your hardest security question or your next customer questionnaire.
Not ready for a call? Email hello [at] trellissecurityadvisors.com